Governance, risk and compliance
Runs your GRC (Governance, risk and compliance. Security policies, the review of risks, and meeting the rules and standards that apply to you.): policies, risks and controls.
Virtual CISO
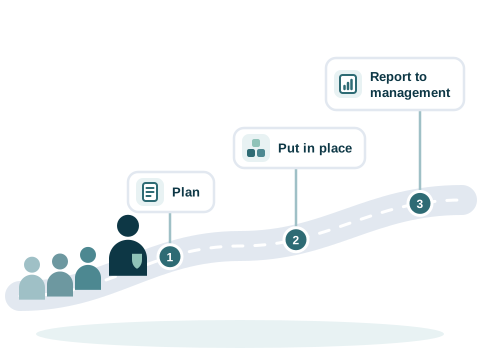
Security leadership as a service, for companies of any size. A virtual CISO (A fractional chief information security officer. Security leadership as a service. A virtual CISO sets your security direction, puts it in place with your team, and reports on it to management.) sets your security direction, puts it in place with your team, and reports on it to management.
Every company needs someone who owns security. A virtual CISO from Visiminds does that job with your team.
Runs your GRC (Governance, risk and compliance. Security policies, the review of risks, and meeting the rules and standards that apply to you.): policies, risks and controls.
Manages the daily work: monitoring, response and improvement.
Plans and supports internal and external security audits, before and during the audit.
Leads cyber forensics and forensic readiness (Being prepared before an incident, so the evidence an investigation needs is collected and kept.), so you are ready for an investigation.
Four engagements from our seven case studies.
Durations are as of September 2026. Case studies 4, 5 and 6 are ongoing. Case study 1 was a one-time engagement.
The work starts with a review, and can go on for years.
A review of your current security. Then a plan: the risk you accept, and the controls to put in place.
Controls and procedures, put in place with your team.
We report to your management on the plan and on the work done.
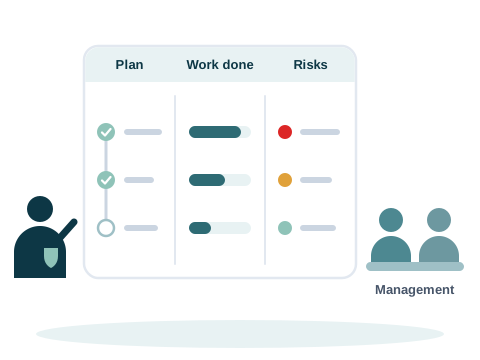
Your management sees the plan, the work done and the risks that are still open.
Ways to work with us
If no one owns security in your company yet, write to info@visiminds.com and we will talk it through.