Governance
How your company decides on security and keeps control of it.
- Security policies and procedures
- Controls chosen and put in place
Security services
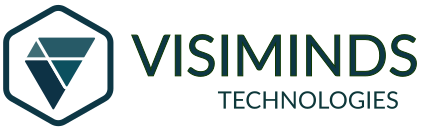
Policies, risks and controls that your customers and auditors can check. Our GRC (Governance, risk and compliance. Security policies, the review of risks, and meeting the rules and standards that apply to you.) work helps with ISO 27001 (ISO/IEC 27001. The international standard for an information security management system.), SOC 2 (An audit of how a service company protects customer data.) and regional compliance, and with the security checklists (The questions a customer sends before it buys, to check how a supplier protects its data.) your customers send.
We shape the work to your company, to your customers, and to the rules of your country or region.
How your company decides on security and keeps control of it.
What could go wrong, and what you decide to do about it.
The standards and rules that apply to you, and your customers' checks.
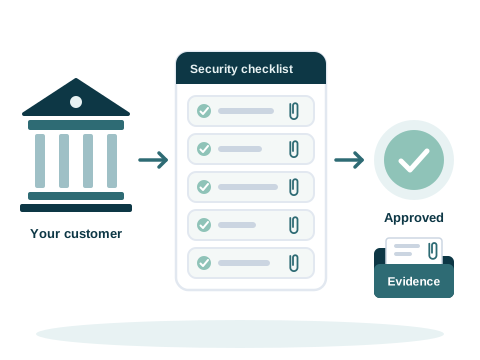
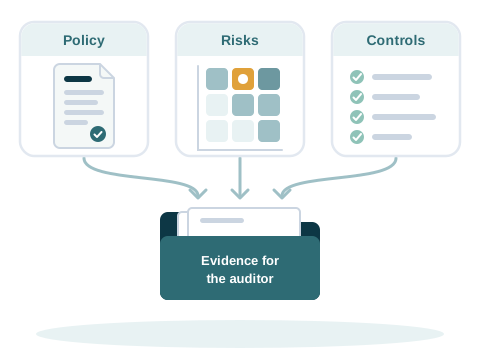
Banks and insurers send security checklists before they buy. We answer them with you, with the evidence each answer needs, through to approval.
A virtual CISO (A fractional chief information security officer. Security leadership as a service. A virtual CISO sets your security direction, puts it in place with your team, and reports on it to management.) can also run your GRC with your team. About the virtual CISO
What our GRC work helps with, and what Ivy Insight maps its findings to. We keep the two apart.
Standards our GRC work has helped clients with.
9 standards, as Visiminds' own mapping, not a statement of compliance. The mapping can be adapted to your needs and to the regulations of your country or region.
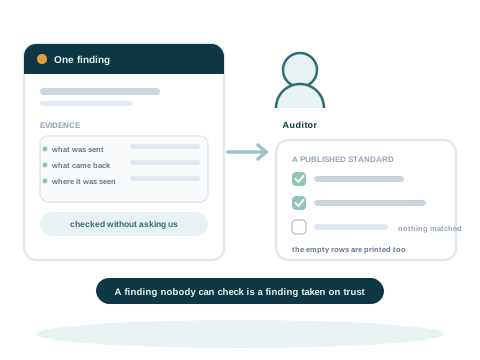
Each Ivy Insight finding keeps the evidence it rests on. Benchmark checks keep the command and its output.
Every report shows what it covered and what it left out, so an auditor can see both.
Case study 6
GRC leadership as part of virtual CISO work, for a large technology startup. The aim was to get its product through the security checks of the top 25 banks and insurers. We worked with its clients on their security checklists, and got the approvals.
Case study 4
Help with ISO 27001 and other regional compliance, as part of our security services for the clients of a large system integrator in the UAE.
Case study 2
A security and process audit for a global cybersecurity company, and the changes needed for SOC 2 compliance. This was part of our joint development work with the company.
See also use case 7: Passing customer security checks, for startups, product companies and companies selling to banks.
An audit to prepare for, a customer checklist, or policies to write: tell us at info@visiminds.com.