Be ready
Before an incident
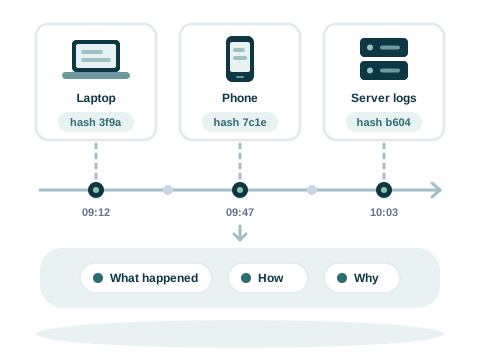
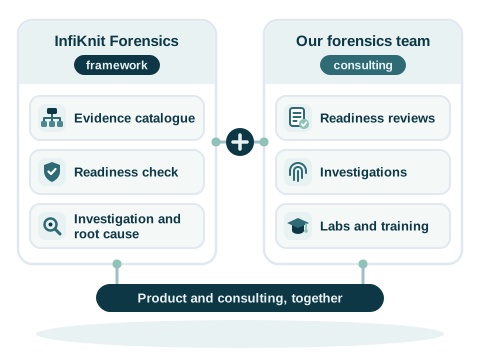
InfiKnit Forensics checks that your organisation can collect the evidence that cyber forensics analysis and DFIR (Digital forensics and incident response. Investigating an incident and handling it, from the first alert to the report.) need. This is forensic readiness (Being prepared before an incident, so the evidence an investigation needs is collected and kept.).
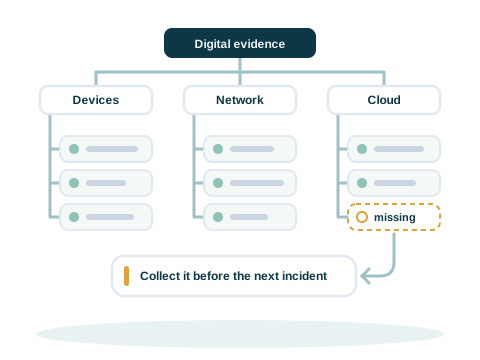
- Classify evidence with a catalogue of evidence types, called an evidence taxonomy (A catalogue that sorts digital evidence into types, so an investigation knows what to look for.)
- Know what you can collect, and what is missing