Virtual CISO
A fractional (Given as a service. One security leader works with several companies, and leads security with each company's team.) chief information security officer, who leads security with your team.
Security consulting from Bengaluru
We offer a virtual CISO (A fractional chief information security officer. Security leadership as a service. A virtual CISO sets your security direction, puts it in place with your team, and reports on it to management.), GRC (Governance, risk and compliance. Security policies, the review of risks, and meeting the rules and standards that apply to you.), VAPT (Vulnerability assessment and penetration testing. Finding the weak spots in apps, APIs, networks and cloud, and testing them the way an attacker would.) and cyber forensics, for companies of any size. We work with your team directly, and train the people who do the work.
Four security services, our 360-degree approach, and training.
A fractional (Given as a service. One security leader works with several companies, and leads security with each company's team.) chief information security officer, who leads security with your team.
Governance, risk and compliance: policies, risk reviews, and help with ISO 27001 (ISO/IEC 27001. The international standard for an information security management system.) and SOC 2 (An audit of how a service company protects customer data.).
Vulnerability assessment and penetration testing of apps, APIs (Application programming interface. The interface one program uses to talk to another.), networks and cloud.
Readiness, investigations and root cause analysis (Root cause analysis. Finding out what happened in an incident, how, and why.), with InfiKnit Forensics.
Assess, define, implement and monitor, wherever you start.
Hands-on courses in cybersecurity, cyber forensics, secure coding and databases.
For large companies and small ones, wherever your security stands today.
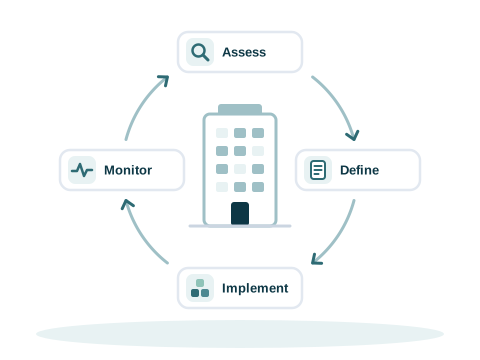
We shape the work to your company. It can cover every area of your security.
What it covers
From our security engagements and our products.
Work can be short or long, for you or for your clients. We agree its shape with you.
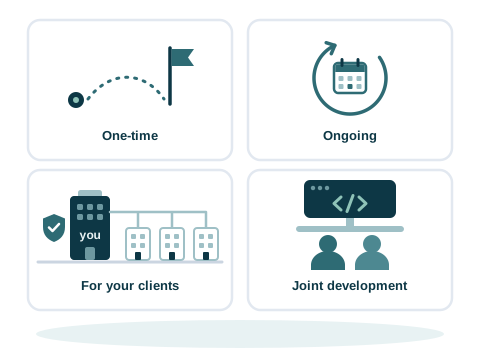
A piece of work with a clear end. For example, a custom VAPT and a risk plan for a finance company.
We stay with your team over time, as a virtual CISO or for testing in rounds.
For system integrators: we carry out the security work for your clients.
We build security tools and products together with your team.
We have carried out security risk assessments for clients in retail, real estate, finance and space, and for many product companies.
Durations are as of September 2026.
To talk about a virtual CISO, GRC, VAPT or cyber forensics, write to info@visiminds.com.