Visiminds Technologies, home

Our work

Case studies

Seven engagements from our cybersecurity and virtual CISO (A fractional chief information security officer. Security leadership as a service. A virtual CISO sets your security direction, puts it in place with your team, and reports on it to management.) work, for clients in finance, technology and other sectors. They cover VAPT (Vulnerability assessment and penetration testing. Finding the weak spots in apps, APIs, networks and cloud, and testing them the way an attacker would.), GRC (Governance, risk and compliance. Security policies, the review of risks, and meeting the rules and standards that apply to you.), ethical hacking (Attacking a system with the owner's permission, to find weaknesses before a real attacker does.), compliance, risk assessment and security tools.
A stack of three engagement reports, each tagged with how long the work ran and with its sector: finance, real estate or technology

The seven cases

Clients are not named. Durations are as of September 2026.

We have also carried out security risk assessments for clients in retail, real estate, finance and space, and for many product companies.

Case study 1

Custom VAPT and a risk plan

Vulnerability assessment and penetration testing designed for the client. Then a plan to reduce the risk, and the work to carry it out.
What we did

  • Testing in several rounds, each deeper than the last
  • After every round, we worked directly with the client's developers to fix the issues
  • The tests covered API (Application programming interface. The interface one program uses to talk to another.) security, payment security, infrastructure security, data storage and retrieval, and secure coding practices
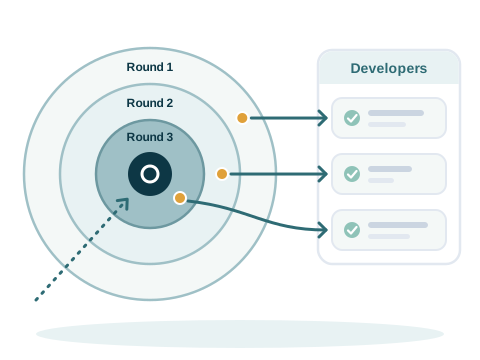
Testing in three rounds shown as three rings around a target, each round going deeper, and after each round an arrow to the developers, who fix what was found

The engagement

Client
A finance company
Engagement
One-time
Duration
1+ month

Services

  • VAPT
  • API testing
  • Payment security
  • Secure coding
  • Risk mitigation

Case study 2

Product and tool development

We develop a product and specialised tools for a cybersecurity company that serves a small market.
What we did

  • Tools to assess the security of thousands of VoIP (Voice over IP. Phone calls over the internet.) and IP telephony servers
  • Security tools for its products, including analysis of large networks
  • Server software that responds in under 10 milliseconds
  • A security and process audit, and the changes SOC 2 (An audit of how a service company protects customer data.) needs
  • Risk assessment models for product integrations
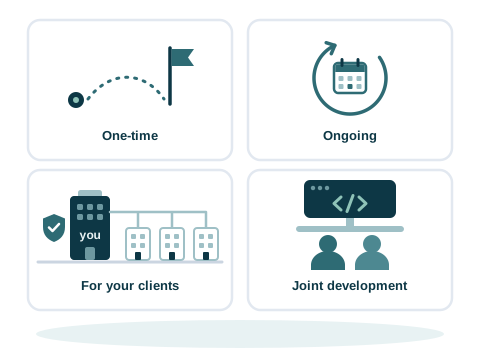
Four tiles for the ways to work with Visiminds: a one-time engagement as a short path to a flag, an ongoing engagement as a loop around a calendar, consultancy to your clients as one company serving three client buildings, and joint development as two people at one code window

The engagement

Client
A global cybersecurity company
Engagement
Joint development and consultancy
Duration
5+ years, ongoing

Services

  • Security tools
  • Network security
  • SOC 2
  • Risk assessment

Case study 3

Ethical hacking and testing

Ethical hacking and penetration testing for a large organisation in India.
What we did

  • Active and passive reconnaissance (Looking for targets: collecting what is known about a system before testing or attacking it.)
  • Vulnerability assessment and penetration testing, including tests for certification
  • Security controls put in place
  • Research on cyber forensics controls, for future process changes
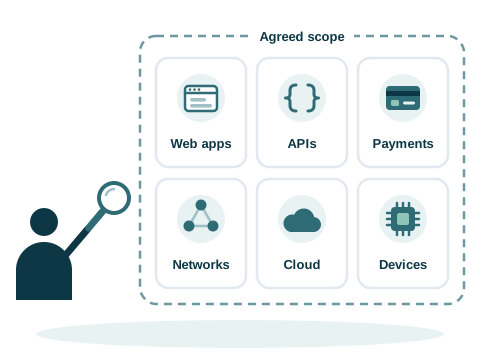
A dashed frame marks the agreed scope around six kinds of target, web apps, APIs, payment systems, networks, cloud servers and devices, and a tester outside the frame checks what is inside it

The engagement

Client
A large organisation in India
Engagement
Joint work, sharing knowledge
Duration
1+ year

Services

  • Ethical hacking
  • VAPT
  • Security controls
  • Cyber forensics

Case study 4

Security services for an integrator's clients

Everything a CISO (Chief information security officer. The person who leads security in a company.) does, for the clients of a large system integrator in the UAE.
What we did

  • VAPT, risk assessment and compliance for each client
  • Fixing issues, including getting fixes from vendors
  • Security scorecards, and readiness for operations
  • Help as needed with ISO 27001 (ISO/IEC 27001. The international standard for an information security management system.) and other regional compliance
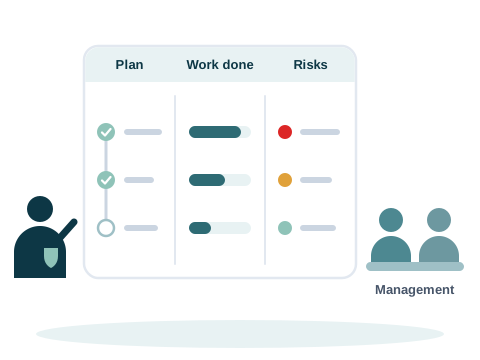
A security lead presents a board to management with three parts: the plan with two of three milestones ticked, the work done as progress bars, and the open risks marked high, medium and low

The engagement

Client
A large system integrator in the UAE
Engagement
Consultancy to the integrator's clients
Duration
5+ years, ongoing

Services

  • Virtual CISO
  • VAPT
  • Risk assessment
  • Compliance
  • ISO 27001

Case study 5

Security architecture, VAPT and a risk plan

Vulnerability assessment and penetration testing designed for the client, and work on its security architecture. We made a plan to reduce the risk, and carried it out.
What we did

  • Helped improve its security architecture
  • Testing in several rounds, each deeper than the last
  • After every round, we worked directly with its developers to fix the issues
  • The tests covered API security, and the security of data storage and retrieval
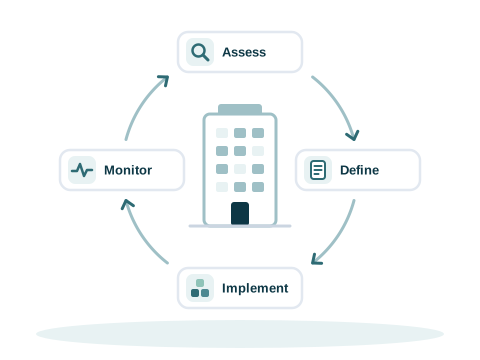
Four steps in a circle around a company building: assess, define, implement and monitor, with arrows leading from each step to the next and back to the start

The engagement

Client
A real estate technology company
Engagement
Ongoing
Duration
3+ years, ongoing

Services

  • VAPT
  • Security architecture
  • API testing
  • Data security

Case study 6

A product made ready for banks and insurers

GRC leadership, as part of our virtual CISO work. The goal was to get the startup's product through the security checks of the top 25 banks and insurance companies.
What we did

  • All of its governance, risk and compliance needs
  • Worked with its clients on their security checklists (The questions a customer sends before it buys, to check how a supplier protects its data.), and got the approvals
  • Developed and improved its architecture
  • High availability and disaster recovery
  • Tools and methods to improve its security posture (The overall state of your security settings and defences.)
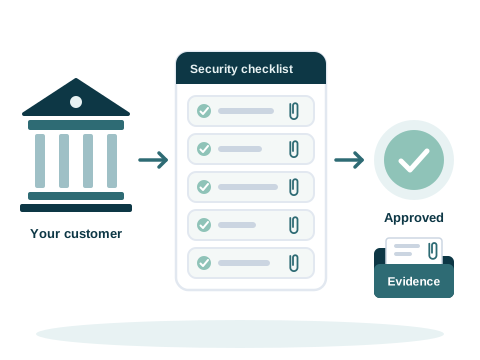
A bank sends a security checklist, each question is answered with its evidence attached, and the checklist comes back approved

The engagement

Client
A large technology startup
Engagement
Ongoing
Duration
1+ year, ongoing

Services

  • GRC
  • Virtual CISO
  • Security checklists
  • Disaster recovery

Case study 7

Ethical hacking of a gaming device

Ethical hacking, a security posture assessment and reporting, for a company in the Netherlands.
What we did

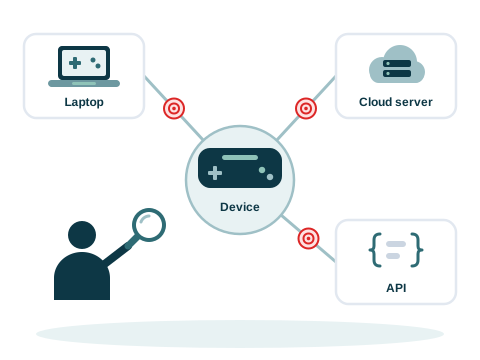
  • Ethical hacking of gaming hardware that uses crypto tokens and plugs into gaming laptops
  • A full security posture assessment, including the APIs and the server in the cloud
  • Detailed reports on the many possible ways to attack the system
A gaming device joined to a gaming laptop, its API and its cloud server, with each link marked as tested for the ways an attacker could get in

The engagement

Client
A gaming hardware company in the Netherlands
Duration
3+ months

Services

  • Ethical hacking
  • Hardware security
  • API testing
  • Cloud security

Tell us what you need

Write to info@visiminds.com. We shape each engagement to your needs and to the regulations of your country or region.