Visiminds Technologies, home

Visiminds Technologies

Security products, consulting and training

A Bengaluru company focused on cybersecurity and cyber forensics. We build security products, lead security work with your team, and train your people.

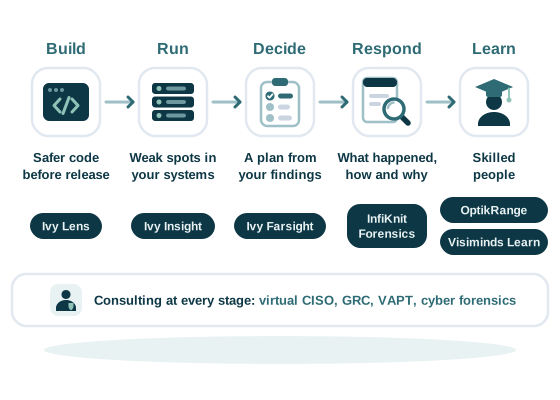
Five stages of security and what Visiminds offers at each: Ivy Lens for safer code before release, Ivy Insight for weak spots in your systems, Ivy Farsight for a plan from your findings, InfiKnit Forensics for what happened in an incident, and OptikRange with Visiminds Learn for skilled people, with consulting at every stage

Three Ivy security products

The code you build, the systems you run, and the findings you already have

Ivy Lens and Ivy Insight complement each other, and each writes its own report on the same severity scale. Ivy Farsight turns the findings you already have into decisions.

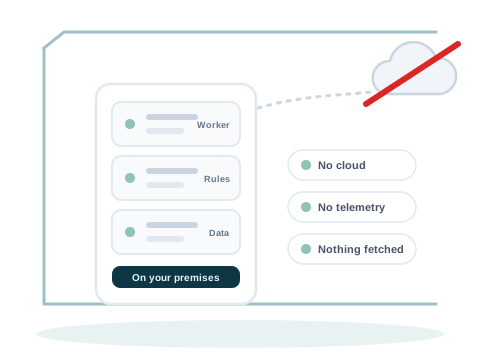
A server on your own premises with the cloud crossed out: no cloud, no telemetry, nothing fetched while a scan runs

Checks the code you build: source code, open source packages, secrets, infrastructure files, and Android and iOS apps. It runs on your own computer.

  • 893 rules written by Visiminds
  • Findings checked against the code, not just listed
  • A report for each reader: developers, the security team and management
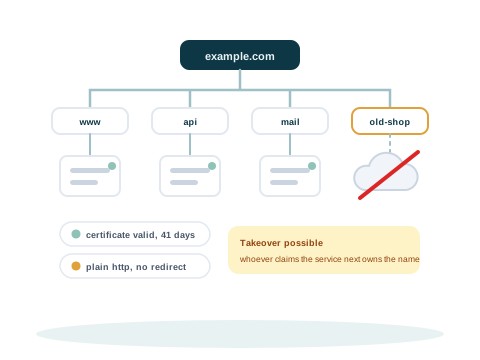
A domain at the top with the names beneath it discovered one by one, and one name still pointing at a cloud service that no longer exists, flagged as a takeover

Checks the systems you run: systems open to the internet, websites, APIs (Application programming interface. The interface one program uses to talk to another.), networks, databases, cloud accounts and AI applications. It can run in your network.

  • 11 engines, run as often as you like
  • Tests against 7 security frameworks
  • A deadline on every finding
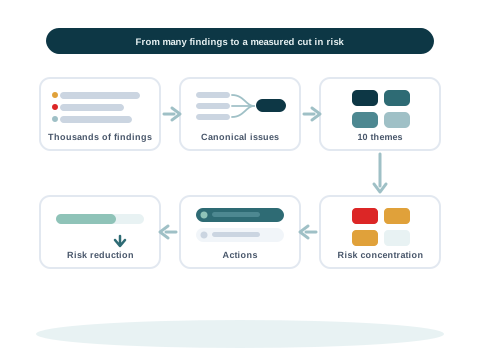
Findings become canonical issues, then themes, then risk concentration, then actions, then a measured risk reduction

Reads the findings you already have, from audits, scanners and reviews. It groups them by cause, shows where the risk sits, and plans the actions that lower it most.

  • Findings grouped into canonical issues (One underlying problem that many findings describe. Findings that agree on their control, threat path, text, assets and timing are grouped into one canonical issue.) and themes
  • A remediation plan for leadership, managers and engineers
  • Every figure opens to its source row

What the 2026 reports say

Many breaches start with an exploited weakness, and these weaknesses take a long time to fix.

31%of the breaches studied began with an exploited weakness, more than any other way inVerizon 2026 Data Breach Investigations Report
43 daysthe median (The middle value. Half of the values are above it, and half are below it.) time to fully fix a weakness that attackers were already using (on CISA's (Cybersecurity and Infrastructure Security Agency. The cybersecurity agency of the United States. It publishes the list of known exploited vulnerabilities.) Known Exploited Vulnerabilities (Known Exploited Vulnerabilities. CISA's list of vulnerabilities that attackers are known to have used.) list), up from 32 days the year beforeVerizon 2026 Data Breach Investigations Report
247 daysthe average time to find and contain a breachIBM Cost of a Data Breach Report 2026

Weaknesses like these can be found in two places: in the code, on every build, and in the systems it runs on, at any time. Ivy Lens checks the first. Ivy Insight checks the second.

Services

Security consulting

Beyond our products, we work with teams directly.

Virtual CISO

A fractional (Given as a service. One security leader works with several companies, and leads security with each company's team.) chief information security officer (CISO (Chief information security officer. The person who leads security in a company.)), who leads security with your team.

Governance, risk and compliance

GRC (Governance, risk and compliance. Security policies, the review of risks, and meeting the rules and standards that apply to you.): policies, risk reviews, and help with ISO 27001 (ISO/IEC 27001. The international standard for an information security management system.) and SOC 2 (An audit of how a service company protects customer data.).

VAPT

Vulnerability assessment and penetration testing (Vulnerability assessment and penetration testing. Finding the weak spots in apps, APIs, networks and cloud, and testing them the way an attacker would.) of apps, APIs, networks and cloud, in rounds.

Cyber forensics

Readiness before an incident, investigations after one, and forensics labs for police and laboratories.

More from Visiminds

Cyber forensics and training

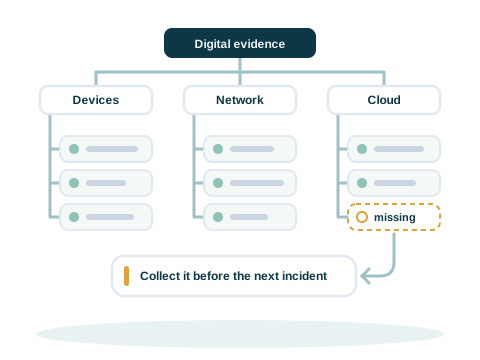
A catalogue of digital evidence types drawn as a tree, with every slot collected except one that is marked missing, and a note to collect it before the next incident

InfiKnit Forensics

Our cyber forensics framework, a product for investigations and root cause analysis (RCA) (Root cause analysis. Finding out what happened in an incident, how, and why.), with consulting from our forensics team. It classifies digital evidence (Information stored or sent in digital form that can be used in an investigation, such as logs, files and messages.) and finds what is missing.

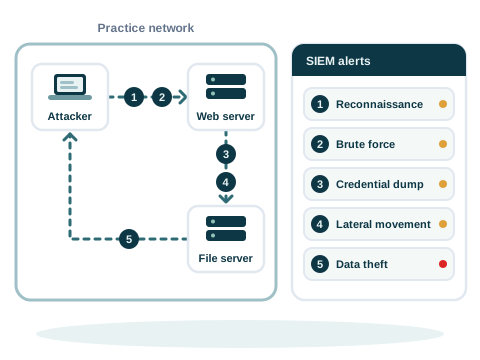
A practice network where an attack runs in five numbered steps, from reconnaissance to data theft, and a SIEM panel beside it that shows an alert for each step

OptikRange

A modular (Built from separate parts, so parts can be added or changed.) cyber range (A practice network where people learn to attack and defend safely.). It runs attack scenarios from beginner to expert level. Each attack raises alerts in a SIEM (Security information and event management. The system that collects security alerts and logs in one place.) while it runs.

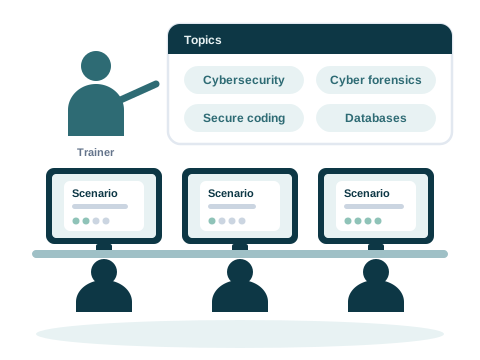
Three learners at screens work through scenario cards, and a trainer points to a board of topics: cybersecurity, cyber forensics, secure coding and databases

Visiminds Learn

Hands-on training with more than 100 tools, for police, enterprise staff and security professionals.

From our work

We have carried out security risk assessments for clients in retail, real estate, finance and space, and for many product companies.

A large system integrator in the UAE

Security services for an integrator's clients

Everything a CISO does, for its clients: VAPT, risk assessment and compliance.

Duration
5+ years, ongoing

A large technology startup

A product made ready for banks and insurers

GRC leadership, to get its product through the security checks of the top 25 banks and insurers.

Duration
1+ year, ongoing

A real estate technology company

VAPT in rounds, and a risk plan

Testing in rounds, each deeper than the last, with its developers after each round, and work on its security architecture.

Duration
3+ years, ongoing

Clients are not named. Durations are as of September 2026.

Tell us what you need

Write to info@visiminds.com. Demos of Ivy Lens, Ivy Insight and Ivy Farsight are on request.